
Query Examples
The following queries are examples of strings you can use to search anything within logs.
Info
You can use boolean operators to add more search parameters.
- As an example, in the following image, you can construct and type the following queries in the search bar.
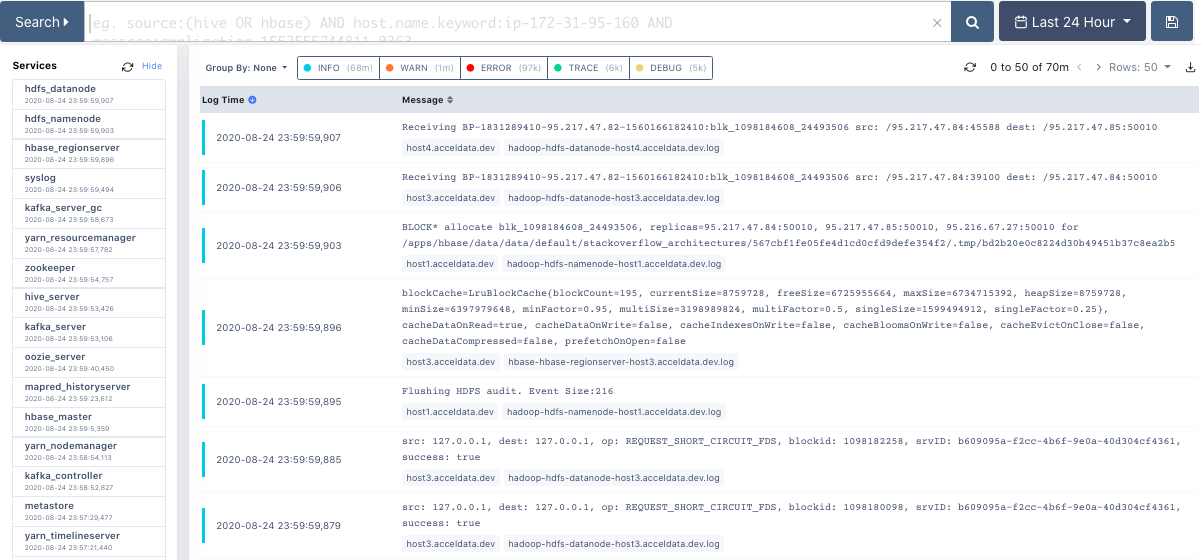
- To search logs by a message string
Receiving BP-18, use the following syntax: [INLINE_CODE]message:< message>[/INLINE_CODE]. For example, [INLINE_CODE]message:Receiving BP-18[/INLINE_CODE] - To search logs by a message string on a particular host, use the following syntax:
message:<message>AND host.name.keyword:<host name>. For example, [INLINE_CODE]Receiving BP-18 AND host.name.keyword:host4.acceldata.dev[/INLINE_CODE] - To search application logs of particular services, use the following syntax:
fields.component:<service name>. For example, [INLINE_CODE]fields.component:hdfs_datanode[/INLINE_CODE].
Search Keywords Allowed
To search within Logs, the following keywords are allowed.
Keyword | Description | Example |
| To search within services. |
|
| To filter search by host name. |
|
| To filter search by source location. |
|
| To search within the log level which can be either Info, Debug, Warn, or Error. |
|
Boolean operators | For an improved search within logs. |
|
Have a suggestion?