
Fixed CVEs
This release resolves xsecurity vulnerabilities (CVEs) identified across ODP platform components, representing a comprehensive security hardening initiative implemented during the upgrade from version 3.3.6.5-1 to 3.3.6.6
Detailed List of CVE Fixes
For detailed information about CVEs addressed in this release, see ODP 3.3.6.6 CVE Fixes.
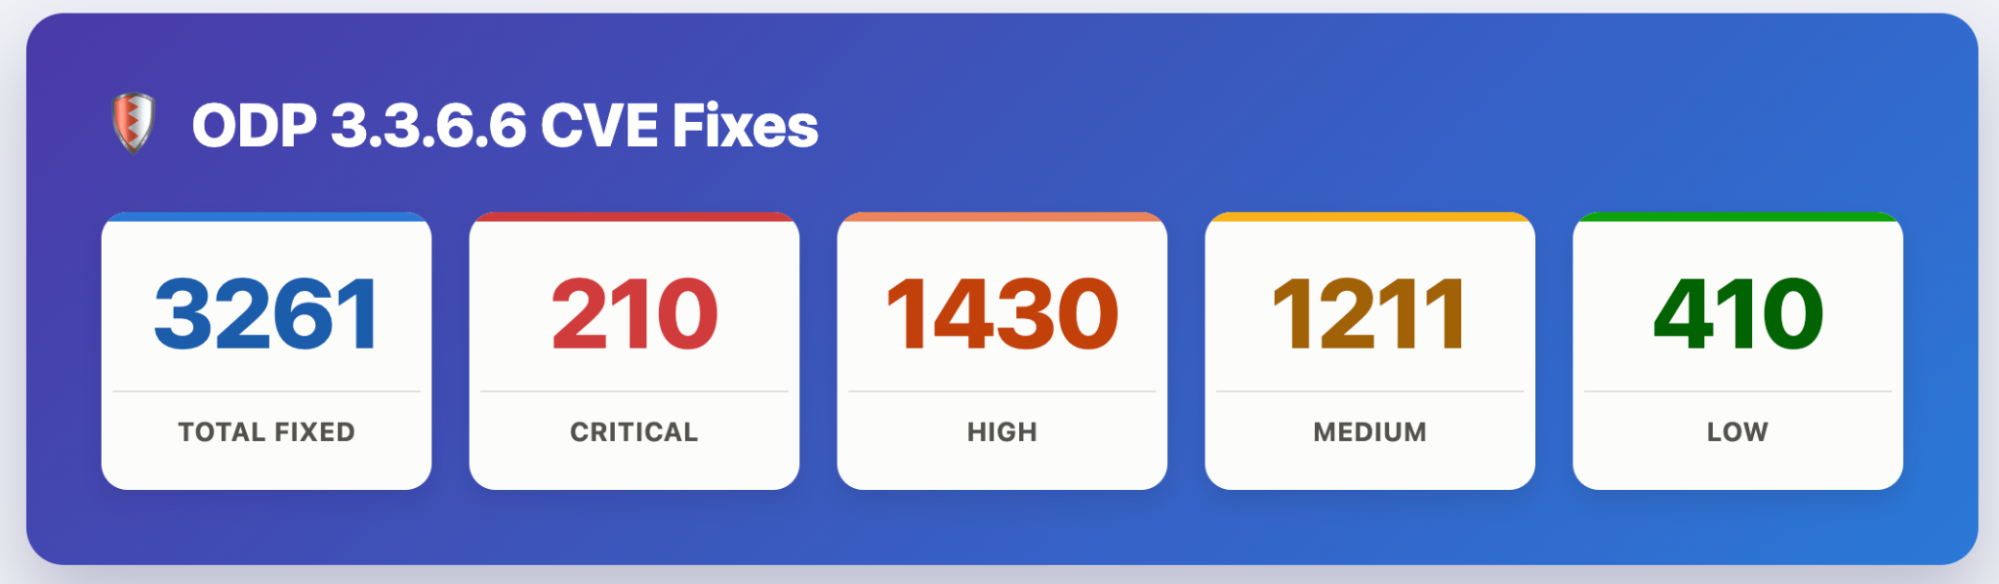
You can see the summary of CVEs addressed by components and severity level.
CVE Fix Descriptions
Airflow
- OSV-41061: Upgraded redshift-connector to 2.1.7.
- OSV-41068: Upgraded cryptography to 48.0.1.
- OSV-41063: Upgraded sqlparse to 0.6.0.
- OSV-41035: Upgraded soupsieve to 2.8.4.
- OSV-41077: Upgraded tornado to 6.5.8.
- OSV-41025: Upgraded aiohttp to 3.14.3.
Celeborn
- OSV-41138: Pinned jackson-annotations to 2.21.
- OSV-41138: Aligned Jackson to 2.21.4.
- OSV-41125: Upgraded JLine to 3.30.14.
- OSV-41122: Upgraded HTTPCore5 to 5.4.3.
- OSV-41138: Upgraded Jackson to 2.18.8.
- OSV-41149: Upgraded Netty to 4.1.137.Final.
- OSV-41138: Fixed Spotless import ordering in TestMemoryConsumer.
Cruise Control
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844. Marked In Progress in the source.
- OSV-41795: Upgraded Jackson to 2.18.8.
- OSV-41793: Upgraded Netty to 4.1.137.Final.
Cruise Control 3
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
Flink
- OSV-39303: Aligned Jackson to 2.21.4.
- OSV-39303 / FLINK-38855: Upgraded Jackson to 2.20.1.
- OSV-39303: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
Hadoop
- OSV-40140: Pinned jackson-annotations to 2.21.
- OSV-40140: Aligned Jackson to 2.21.4.
- OSV-40145: Upgraded JLine to 3.30.14 to address CVE-2025-66560.
- OSV-40159 / HADOOP-19957: Upgraded Netty to 4.1.137.
- OSV-40140 / HADOOP-19967: Upgraded Jackson to 2.18.10.
HBase
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
- OSV-39345: Pinned jackson-annotations to 2.21.
- OSV-39345: Aligned Jackson to 2.21.4.
- OSV-39327: Upgraded bcprov-jdk18on to 1.80.2 to address CVE-2025-8916.
- OSV-39342: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
Hive
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844. Marked In Progress in the source.
- OSV-38535: Aligned Jackson to 2.21.4.
- OSV-38533: Upgraded commons-beanutils to 1.11.0 to address CVE-2025-48734.
- OSV-38536: Upgraded Ant to 1.10.18 to address CVE-2025-59335.
- OSV-38614: Upgraded Guava to 32.0.0 to address CVE-2023-2976.
- OSV-38535: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-38621: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
Hue
- OSV-35995: Upgraded Django to 4.2.30.
- OSV-36014: Upgraded Thrift to 0.24.0.
- OSV-36019: Upgraded cryptography to 50.0.1.
- OSV-36020: Upgraded PyJWT to 2.12.0.
- OSV-36026: Upgraded sqlparse to 0.5.4.
- OSV-38462: Upgraded sqlparse to 0.6.0.
Impala
- OSV-40281: Pinned jackson-annotations to 2.21.
- OSV-40281: Aligned Jackson to 2.21.4.
- OSV-40281: Upgraded Jackson to 2.18.8.
- OSV-40357: Upgraded Netty to 4.1.137.Final.
Infra Solr
- OSV-44183: Replaced AWS SDK third-party-jackson-core 2.17.63 with 2.54.17 in bundled Solr.
- OSV-44769: Upgraded velocity-engine-core from 2.3 to 2.4.1.
- OSV-44769: Upgraded commons-lang3 from 3.10 to 3.18.0.
- OSV-44771: Upgraded commons-io from 2.11.0 to 2.22.0.
- OSV-44126: Upgraded Netty from 4.1.99.Final to 4.1.138.Final.
- OSV-44269: Upgraded Jackson from 2.15.2 to 2.18.11.
- OSV-44807: Excluded Logback from ambari-infra-solr-client.
- OSV-44125: Upgraded AWS SDK v2 bundle to 2.54.17.
- OSV-44096: Upgraded Swagger UI WebJar to 4.1.3.
- OSV-44622: Removed bcprov-jdk15on 1.61.
- OSV-44150: Upgraded sqlite-jdbc to 3.41.2.2.
- OSV-44123: Upgraded FreeMarker to 2.3.35.
- OSV-44607: Upgraded hibernate-validator to 6.0.23.Final.
- OSV-44410: Upgraded Jettison to 1.5.4.
- OSV-44086: Upgraded SnakeYAML to 2.0.
- OSV-44444: Aligned Spring Framework modules to 5.1.18.RELEASE.
- OSV-44439: Upgraded Jetty to 9.4.57.v20241219.
- OSV-44184: Upgraded XStream to 1.4.21.
- OSV-44761: Upgraded commons-io to 2.22.0.
- OSV-44387: Upgraded commons-fileupload to 1.6.0.
- OSV-44362: Upgraded Log4j to 2.25.5.
- OSV-44261: Upgraded Jackson to 2.18.11.
JupyterHub
- OSV-41551: Upgraded msgpack to 1.2.1.
- OSV-41510: Upgraded mistune to 3.3.0.
- OSV-41528: Upgraded Ray to 2.56.0.
- OSV-41549: Upgraded JupyterLab to 4.5.10.
- OSV-41534: Upgraded Keras to 3.15.0.
- OSV-41541: Upgraded Pillow to 12.3.0.
- OSV-41531: Upgraded soupsieve to 2.8.4.
- OSV-41538: Upgraded tornado to 6.5.8.
- OSV-41509: Upgraded aiohttp to 3.14.3.
Kafka 2
- OSV-39391: Adapted Kafka Scala core to Jackson 2.21 APIs.
- OSV-39391: Adapted Kafka to Jackson 2.21 APIs.
- OSV-39391: Pinned jackson-annotations to 2.21.
- OSV-39391: Aligned Jackson to 2.21.4.
- OSV-39400: Upgraded JLine to 3.30.14.
- OSV-39391: Upgraded Jackson to 2.18.8.
- OSV-39447: Upgraded Netty to 4.1.137.Final.
Kafka 3
- OSV-40483: Adapted Kafka 3 Scala core to Jackson 2.21 APIs.
- OSV-40483: Adapted Kafka 3 to Jackson 2.21 APIs.
- OSV-40483: Pinned jackson-annotations to 2.21.
- OSV-40483: Aligned Jackson to 2.21.4.
- OSV-40458: Upgraded JLine to 3.30.14.
- OSV-40483: Upgraded Jackson to 2.18.8.
- OSV-40408: Upgraded Netty to 4.1.137.Final.
Kafka 4
- OSV-40474: Pinned jackson-annotations to 2.21.
- OSV-40483: Upgraded JLine to 3.30.14.
- OSV-40415: Upgraded Jetty to 12.0.36.
- OSV-40474: Aligned Jackson to 2.21.4.
Knox
- OSV-38708: Aligned Jackson to 2.21.4.
- OSV-38673: Upgraded Mina to 2.0.29.
- OSV-38702: Upgraded Netty to 4.1.137.Final.
- OSV-38708 / KNOX-3383: Upgraded Jackson to 2.18.9.
Kudu
- OSV-38724: Pinned jackson-annotations to 2.21.
- OSV-38724: Aligned Jackson to 2.21.4.
- OSV-38724: Upgraded Jackson to 2.18.8.
- OSV-38713: Upgraded Netty to 4.1.137.Final.
Livy
- OSV-39529: Pinned jackson-annotations to 2.21.
- OSV-39529: Aligned Jackson to 2.21.4.
- OSV-39570: Upgraded JLine to 3.30.14.
- OSV-39529: Upgraded Jackson to 2.18.8.
- OSV-39566: Upgraded Netty to 4.1.137.Final.
NiFi
- OSV-38921: Pinned jackson-annotations to 2.21.
- OSV-38810: Upgraded Undertow to 2.2.39.Final.
- OSV-38800: Upgraded JLine to 3.30.14.
- OSV-38822: Upgraded Netty to 4.1.137.Final.
- OSV-38921: Upgraded Jackson to 2.21.4.
NiFi 2
- OSV-39693: Upgraded JLine to 3.30.14.
- OSV-39653: Upgraded Spring Security to 6.5.11.
- OSV-39691: Upgraded Spring Framework to 6.2.19.
- OSV-39661: Upgraded Jetty to 12.1.10.
- OSV-39660: Upgraded Netty to 4.2.17.Final.
- OSV-39692: Upgraded Jackson to 2.21.4.
Oozie
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
Ozone
- OSV-40530: Excluded legacy jaxb-api from jackson-module-jaxb-annotations.
- OSV-40499: Upgraded JLine to 3.30.14.
- OSV-40530: Upgraded Jackson to 2.21.4.
- OSV-40504: Upgraded Netty to 4.1.137.Final.
Ranger
- OSV-40721: Pinned jackson-annotations to 2.21.
- OSV-40739: Upgraded embedded Tomcat to 9.0.121.
- OSV-40730: Upgraded Netty to 4.1.137.Final.
- OSV-40721: Upgraded Jackson to 2.21.4.
Spark 3
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844. Marked In Progress in the source.
- ODP-7835: Updated dependency library versions in the POM.
- OSV-40906: Pinned jackson-annotations to 2.21.
- OSV-40906: Aligned Jackson to 2.21.4.
- OSV-40886: Upgraded jline-remote-telnet to 3.30.14 to address CVE-2026-56740.
- OSV-40849: Upgraded aircompressor to 2.0.3 to address CVE-2024-36114.
- OSV-40906: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-40885: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
Spark 3.3.3
The source service identifier is spark3_3_3_3_3.
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
- ODP-7835: Updated dependency library versions in the POM.
- OSV-41697: Pinned jackson-annotations to 2.21.
- OSV-41697: Aligned Jackson to 2.21.4.
- OSV-41690: Upgraded jline-remote-telnet to 3.30.14 to address CVE-2026-56741.
- OSV-41697: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-41715: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
- ODP-7930 / ODP-7894: Changed the Hive dependency version to 2.3.104.
Spark 3.5.1
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
- ODP-7835: Updated dependency library versions in the POM.
- OSV-41755: Pinned paranamer to 2.8 for Java 8 bytecode compatibility.
- OSV-41755: Pinned jackson-annotations to 2.21.
- OSV-41755: Aligned Jackson to 2.21.4.
- OSV-41773: Upgraded jline-remote-telnet to 3.30.14 to address CVE-2026-56741.
- OSV-41755: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-41774: Upgraded Netty to 4.1.137.Final to address CVE-2026-59901.
Spark 4
- OCR-2627: Upgraded Log4j to 2.25.5 to address CVE-2026-49844.
- ODP-7835: Updated dependency library versions in the POM.
- OSV-41014: Upgraded JLine to 3.30.14.
- OSV-40958 / SPARK-55688: Upgraded aircompressor to 2.0.3.
- OSV-41020 / SPARK-57273: Upgraded Jackson to 2.21.4.
- OSV-41020 / SPARK-57019: Upgraded Jackson to 2.21.3.
- OSV-41020 / SPARK-56156: Upgraded Jackson to 2.21.2.
- OSV-40999 / SPARK-58607: Upgraded Netty to 4.2.17.Final.
- OSV-41016 / SPARK-58041: Upgraded Netty to 4.2.16.Final.
- OSV-40998 / SPARK-57320: Upgraded Netty to 4.2.15.Final.
Sqoop
- OSV-40040: Pinned jackson-annotations to 2.21.
- OSV-39778: Upgraded Tomcat from 9.0.106 to 9.0.121.
- OSV-40040: Aligned Jackson to 2.21.4.
Superset
- OSV-41240: Upgraded msgpack to 1.2.2.
- OSV-41239: Upgraded brotli to 1.2.0.
- OSV-41223: Upgraded markdown to 3.8.1.
- OSV-41241: Upgraded mako to 1.3.12.
- OSV-41236: Upgraded urllib3 to 2.6.3.
Tez
- OSV-38528: Aligned Jackson to 2.21.4.
- OSV-38496: Upgraded jline-remote-telnet to 3.30.14 to address CVE-2025-66560.
- OSV-38528: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-38523: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
Trino
- OSV-40094: Upgraded Apache HTTPCore5 to 5.4.3.
- OSV-41785: Upgraded Jetty to 12.0.36.
- OSV-40100: Upgraded Netty to 4.1.137.Final.
- OSV-40088: Aligned Jackson to 2.21.4.
Zeppelin
- OSV-41385: Aligned Jackson to 2.21.4.
- OSV-41320: Upgraded Jersey to 3.1.10.
- OSV-41368: Upgraded Mina to 2.0.29.
- OSV-41383: Upgraded Netty codec-http2 to 4.1.137.Final.
ZooKeeper
- OSV-41397: Aligned Jackson to 2.21.4.
- OSV-41397: Upgraded Jackson to 2.18.8 to address GHSA-r7wm-3cxj-wff9.
- OSV-41400: Upgraded Netty to 4.1.137.Final to address CVE-2026-75595.
Have a suggestion?